


Research Group

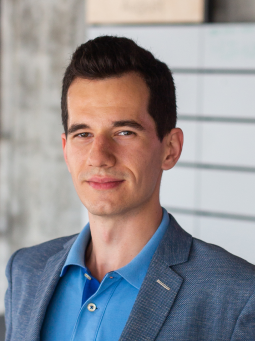
Patrik Goldschmidt
Research areas: computer network security, network anomaly and intrusion detection, cybersecurity data analysis and quality evaluation, transfer learning for cybersecurity applications, machine learning and artificial intelligence for cybersecurity
Position: Volunteer
Patrik is a researcher and Ph.D. student at KInIT, doing his Ph.D. at the Faculty of Information Technology, Brno University of Technology. He specializes in computer networking and information system security, using artificial intelligence and machine learning. He mainly focuses on data-centric aspects of artificial intelligence, including proper handling and quality. He currently researches transfer learning in the network intrusion detection domain, aiming to improve network attack detection by exploring augmentation strategies across different datasets. In 2025, he authored a survey on network intrusion detection datasets, which quickly gained popularity in the research domain. He is the author of NIKTEF, a framework for evaluating knowledge transfer in a cross-domain network intrusion detection setup. From the perspective of industrial cooperation, he worked on anomaly detection in large-scale networks, payment transaction fraud detection, and malicious domain detection, to name a few.
Patrik obtained both his Bachelor’s and Master’s degrees from the Faculty of Information Technology, Brno University of Technology. During these studies, he focused primarily on DDoS attack detection and mitigation as an R&D engineer at CESNET z.s.p.o. Both his Bachelor’s and Master’s theses discussed DDoS mitigation – the first using traditional and the latter utilizing machine learning techniques.
Besides network security, his other professional interests include data science, penetration testing, digital forensics, and parallel algorithms. When not saving the World from cyber-attacks, Patrik likes to enjoy good-quality tea, Yerba maté, ceremonial cacao, or, essentially, any drink with great taste and the potential to boost one’s mood and mind. Patrik embraces lifelong learning, attending various events and talks, listening to podcasts, and reading non-fiction books to broaden his horizons and be better today than the day before.
Selected Achievements
- 2nd best diploma thesis in an Czechoslovak competition at IT SPY 2021
- Dean’s award for Bachelor’s (2019) and Master’s (2021) theses at Faculty of Information Technology, Brno University of Technology, Czechia
Selected Activities
- Research visit at National Institute for Research in Digital Science and Technology (INRIA) in Rennes, France throughout April – August 2024: https://tailor-network.eu/exploring-intrusion-detection-knowledge-transfer-between-network-environments/
- Author of NIKTEF, a framework for cross-domain transfer learning evaluation for network intrusion detection datasets: https://github.com/xGoldy/niktef.
Professional Service
- Reviewer for IEEE Networking Letters (2026)
- Reviewer for IEEE Software (2026)
PhD topic: Data-centric AI for Network Intrusion Detection
Supervising team: Daniela Chudá (KInIT)
Nowadays, many types of cyberattacks aiming to compromise information systems exist in-the-wild. In order to protect information and communication infrastructure, these attacks must be detected and prevented from succeeding. Such goals are typically achieved by Intrusion Detection Systems (IDSs), which monitor the target system or a network and alert on potential malicious or anomalous behavior. Our research focuses on the domain of network intrusion detection using machine learning (ML). ML utilization has greatly improved attack detection capabilities and made the systems significantly more flexible. However, machine learning is heavily dependent on the data, which is one of the main issues within the domain currently. In order to address the data problem, our research aims to pursue the three areas of interest built around the data-centric artificial intelligence approach. Research efforts will be focused on data augmentation, feature engineering, and transfer learning. By achieving these preset research goals, we believe that ML-based IDSs will become more robust by training on higher-quality data and, thus, be more viable for real-world usage.
Selected Projects


Selected Publications
Network intrusion datasets: A survey, limitations, and recommendations
<!---->Goldschmidt, P., Chudá, D. Data-driven cyberthreat detection has become a crucial defense technique in modern cybersecurity. Network defense, supported by Network Intrusion Detection Systems (NIDSs), has also increasingly adopted data-driven…
Windower: Feature Extraction for Real-Time DDoS Detection Using Machine Learning
<!---->Goldschmidt, P., Kucera, J.1 Distributed Denial of Service (DDoS) attacks are an ever-increasing type of security incident on modern computer networks. To tackle the issue, we propose Windower, a feature-extraction…